
AI-Enhanced Business-IT Alignment
Discover how AI can support business-IT alignment, collaboration, and strategic integration to improve organizational efficiency.
14 min read
Software security is critical to keeping information secure and achieving the desired level of cybersecurity, and this can only be accomplished by implementing the appropriate security and specialized practices at all stages of the software development life cycle (SDLC). We are surrounded by interconnected computers (including embedded systems) that run software that can be exploited for unintentional or malicious use, causing serious damage to society or business. Network security is ineffective at reducing the risk of these threats, and software security practices should be implemented throughout all phases of the software life cycle (from software requirements analysis to software qualification testing). This article provides an overview of the practices that should be followed at all stages of the software life cycle.
Keywords: software security, Static Analysis, Dynamic Analysis, Binary Analysis, Secure Requirements, software vulnerabilities, Software Defects, Software Life Cycle, application software.
A computer is a functional unit that can perform significant computations, such as numerous arithmetic and logic operations, without the need for human intervention [1]. A computer is made up of hardware and software.
Hardware refers to the physical components that can be seen and touched (e.g., hard drive, mouse, keyboard, etc.).
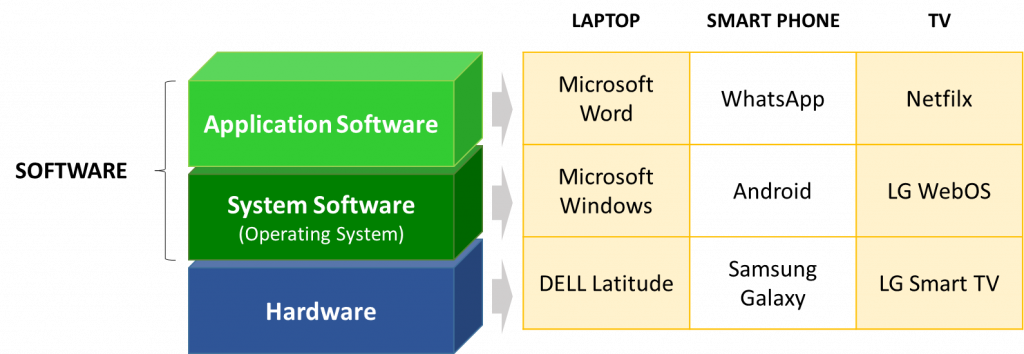
Software (also known as a computer program) is a set of instructions and data definitions that allows a computer to perform computational or control functions (i.e., arithmetic operations and logic operations without human intervention). Software may contain procedures, as well as associated documentation and data, pertaining to the operation of a computer system [1]. Software can be classified according to its intended use. System software and application software are the two main types of software. System software, such as the operating system, is software designed to manage the computer itself. Application software, as opposed to system software, is software designed to assist users in performing specific tasks or dealing with specific types of problems [1]. Figure 1 depicts three examples of common computers and software. More examples of computers (i.e., embedded systems) in our daily lives can be found in my article embedded systems Security [9].
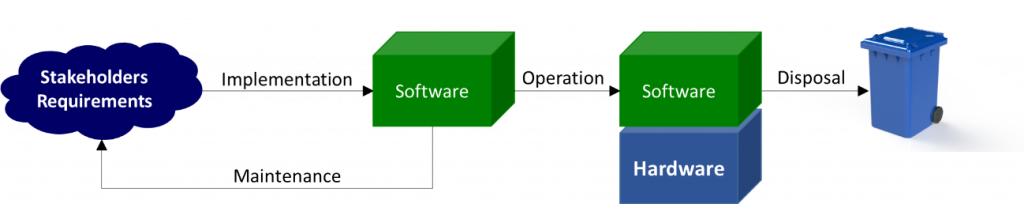
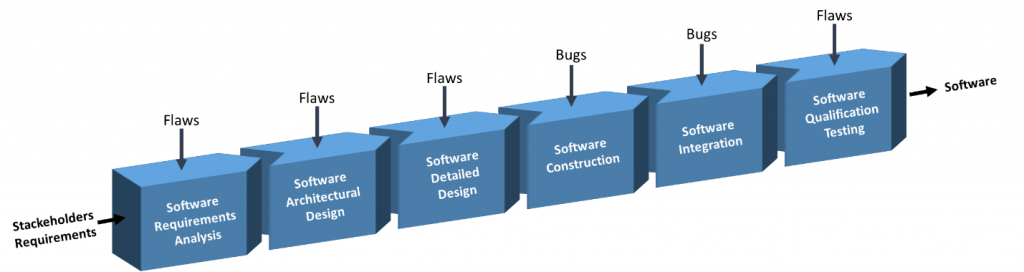
Software is created through a process known as software implementation (also known as the software development life cycle, or SDLC) that transforms the requirements and constraints of specific stakeholders (e.g., users, owners, operators) into intermediate elements through coordinated activities. The software that meets the initial requirements and constraints through verification and validation is the end result of the software implementation process. The primary activities of the software implementation process (Figure 3) are software requirements analysis, software architectural design, software detailed design, software construction, software integration, and software qualification testing, with the following goals in mind [5]:
There are additional support processes that we are not listing here for the sake of brevity.
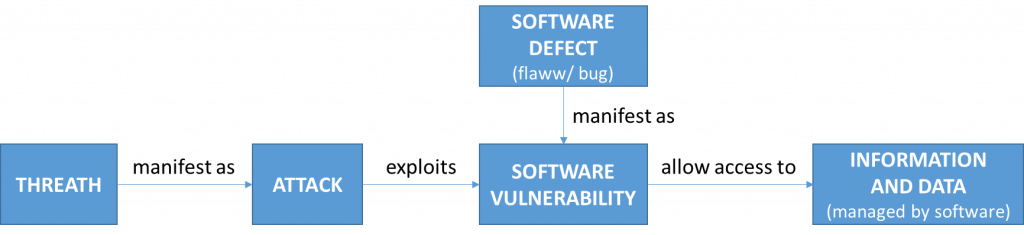
Software vulnerabilities are caused by software flaws introduced during the software implementation process (Figure 3). Bugs are software defects introduced during the software construction and software integration phases, whereas flaws are software defects introduced during the software requirements analysis, software architectural design, and software detailed design phases [7].
As shown in Figure 4, it is useful at this point to summarize the main elements introduced thus far, as well as their relationships.
We are surrounded by interconnected computers (including embedded systems) that run software that can be exploited for unintentional or malicious use, causing serious damage to society or business. Network security is ineffective at reducing the risk of these threats, and software security practices should be implemented throughout all phases of the software life cycle (from software requirements analysis through software qualification testing).
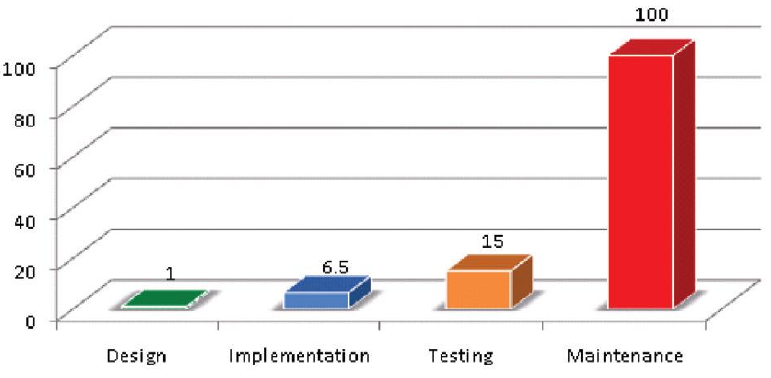
Early detection and correction of software defects during implementation are critical for increasing overall software security and lowering software production costs. According to studies, fixing a defect (or vulnerability) introduced during the early stages of software implementation would cost 6 times more if discovered during software construction/integration, 15 times more if discovered during software testing, and 100 times more if discovered during software maintenance.
[1] ISO/IEC/IEEE 24765 Systems and software engineering — Vocabulary.
[2] ISO/IEC 9126 Software engineering — Product quality.
[3] National Information Assurance (IA) Glossary, Committee on National Security Systems (CNSS), 2015.
[4] ISO/IEC 27002 Information technology — Security techniques — Code of practice for information security controls.
[5] ISO/IEC 12207 Systems and software engineering — Software life cycle processes.
[6] Integrating Software Assurance into the Software Development Life Cycle (SDLC) – Maurice Dawson, Darrell Norman Burrell, Emad Rahim, Stephen Brewster, 2010.
[7] Secure Software Engineering: Learning from the Past to Address Future Challenges – Daniel Hein, Hossein Saiedian, 2009.
[8] ISO/IEC/IEEE 90003 Software engineering — Guidelines for the application of ISO 9001 to computer software.
[9] Embedded Systems Security – Andrea DeSantis, 2020.
Discover how AI can support business-IT alignment, collaboration, and strategic integration to improve organizational efficiency.
A basic checklist for hardening and optimizing a WordPress website.
Explore the role of business stakeholders in cybersecurity and how they can assess the security of the IT/OT systems they own.
CONTINUE THE CONVERSATION
Share your perspective.
Comments are moderated before publication.