
AI-Enhanced Business-IT Alignment
Discover how AI can support business-IT alignment, collaboration, and strategic integration to improve organizational efficiency.
14 min read
Cyber Security / Systems & Software Engineering
Identifying software security vulnerabilities is often difficult. To make the process easier to understand, this article presents a reference model, databases, metrics, and the relationships among CVE, CVSS, CWE, CWSS, OWASP, and SANS. Many organizations and communities create and maintain a wide range of standards, databases, metrics, and classifications in order to identify, describe, publicize, and assess the severity of software vulnerabilities. Because of this plethora of entities and information, it is frequently difficult to understand the distinctions and relationships between them. The purpose of this article is to clarify these.
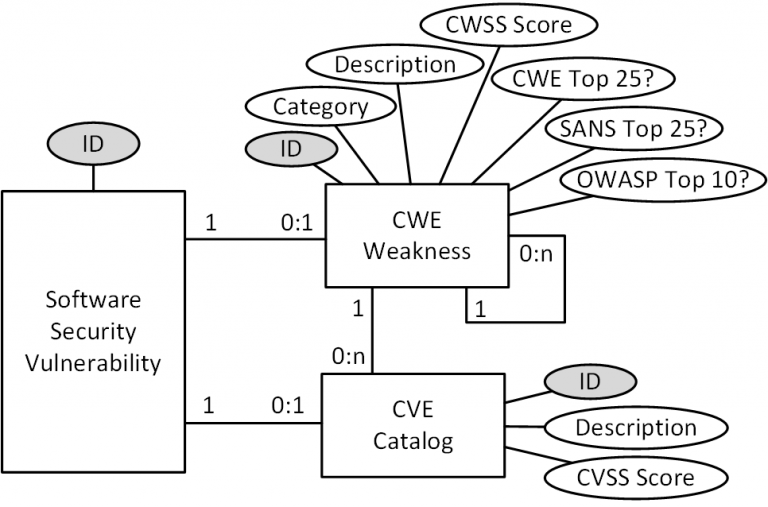
Common Weakness Enumeration (CWE) [1] – This is a list of types of vulnerabilities and defects in software and hardware, developed and maintained by the international community that serves as a common language, a yardstick for security tools, and a basis for identifying, preventing, and mitigating vulnerabilities and defects. Each type of vulnerability in this list has a unique identifier, belongs to a category, has a description, and has a numerical severity calculated through a specific metric (CWSS – Common Weakness Scoring System) [2] based on three sub-metrics: Base Finding, Attack Surface, and Environmental. The twenty-five vulnerability types with the highest CWSS severity are included in a list called CWE Top 25 [3].
Common Vulnerability Scoring System (CVSS) [5] – It is a free and open industry standard for assessing the severity of security vulnerabilities in information systems. The CVSS provides a metric and quantitative measure of the severity of a specific vulnerability with values between 0 and 10 and is considered the current standard for measuring and modeling risk related to application vulnerabilities. The severity measure is composed of a base score (CVSS Base Score [6]) and optional temporal and environmental scores that account for the availability of mitigations and the prevalence of vulnerable systems within an organization, respectively.
Open Web Application Security Project (OWASP) [7] – This is an online community that produces freely available articles, methodologies, documentation, tools, and technologies in the field of web application security, including OWASP Top 10 and OWASP Mobile Top 10.
OWASP Top 10 [8] is a list of the ten web application vulnerability classes (not all software applications) that expose you to the greatest security risks. Risk is calculated based on a combination of vulnerability frequency, vulnerability severity, and potential impacts. The vulnerability list is created, reviewed, and approved by an international community of security experts.
OWASP Mobile Top 10 [9] is a list of the ten mobile application vulnerability classes (not all software applications) that expose you to the greatest security risks. Risk is calculated based on a combination of vulnerability frequency, vulnerability severity, and potential impacts. The vulnerability list is created, reviewed, and approved by an international community of security experts.
SANS [10] – This privately owned company specializing in cybersecurity training periodically produces the SANS Top 25 report [11]. Based on its analysis and evidence, the report lists the twenty-five vulnerability classes that pose the greatest security risks across software applications. Risk is calculated using a combination of vulnerability frequency, severity, and potential impacts. The vulnerability list is created, reviewed, and approved by an international community of security experts. The list of vulnerabilities in the SANS Top 25 [3] report is almost identical to the list of vulnerabilities in the CWE Top 25 report [3].
Software security vulnerabilities can be identified and analyzed either statically or dynamically. In the first case, the software is examined without executing the program, while in the second case it is examined by executing the program. For the purposes of this article, we will focus on static methods, specifically static analysis and software composition analysis.
Static analysis of source code, also known as static analysis or SAST, is a method for identifying and analyzing security vulnerabilities in software that involves examining the code without running the program. Typically, this activity is performed with the help of automated tools (SAST tools) that, in addition to providing an understanding of the code structure, help identify security vulnerabilities and nonconformities present in the software and ensure that the software adheres to international security standards.
Software composition analysis, also referred to as software dependency analysis or SCA for short, is a method for identifying and analyzing the security of software components (for the purposes of this article, OSS frameworks and libraries) that is performed by examining the code without running the program. Typically, this activity is performed with the help of automated tools (SCA tools) that identify and analyze open-source frameworks and libraries that are contained in and used by the software, including related artifacts such as containers and registries. In addition to identifying the security vulnerabilities of these components, noncompliance in terms of licensing and applicability within the organization is also identified. The SCA tool generates an inventory report of all open-source components present in the scanned software, including all direct and transitive dependencies. Once all open-source components have been identified, the tool provides information about each component, including license details, attribution requirements, and whether that license is compatible with the organization’s policies. One of the key functions of the SCA tool, moreover, is to identify open-source components with known vulnerabilities, which allows you to assess and plan for a possible upgrade or replacement of those components.
[1] Common Weakness Enumeration (CWE)
[2] Common Weakness Scoring System (CWSS)
[3] CWE Top 25
[4] Common Vulnerabilities and Exposures (CVE)
[5] Common Vulnerability Scoring System (CVSS)
[6] CVSS Base Score
[7] Open Web Application Security Project (OWASP)
[8] OWASP Top 10
[9] OWASP Mobile Top 10
[10] SANS
[11] SANS Top 25
[12] Software Security, Andrea DeSantis, 2020.
Discover how AI can support business-IT alignment, collaboration, and strategic integration to improve organizational efficiency.
A basic checklist for hardening and optimizing a WordPress website.
Explore the role of business stakeholders in cybersecurity and how they can assess the security of the IT/OT systems they own.
CONTINUE THE CONVERSATION
Share your perspective.
Comments are moderated before publication.