WordPress Hardening & Optimization Checklist
A basic checklist for hardening and optimizing a WordPress website.
2 min read
This article discusses the role of business stakeholders in cybersecurity and how they can assess the security of the IT/OT systems they own. Business stakeholders must participate in the organization’s overall cybersecurity program. They should not delegate overall responsibility for the cybersecurity of the IT/OT systems they own, whether existing or planned, to technical personnel.
Fearful of the growing number of publicly disclosed cybersecurity attacks and incidents, business personnel are increasingly asking their technical colleagues an ostensibly simple question, expecting a simple answer: “How secure is this IT system?”
Business stakeholders already know that this question is rhetorical, that the answer is not as simple as they expect, and that asking it causes frustration and tension with technical staff. Yet they keep asking, and the organization frequently does nothing to make the discussion easier the next time.
This article is intended for business professionals. I’ll try to answer their seemingly rhetorical, straightforward question in their own language and provide some food for thought.
A word to the wise for those in the technical field.
To appropriately respond to the question “How secure is this IT system?”, both the questioner and the responder must first define a common metric for measuring the cybersecurity level of an IT system.
This is similar to asking, “How far is it?” Both parties need to use the same measurement system, such as metric or imperial units. A predefined, shared metric removes ambiguity, enables accurate and timely measurements and responses, and helps avoid frustration and conflict.
The cybersecurity risk metric measures the security of an IT system and helps answer the question, “How secure is this IT system?” Figure 1 presents a simplified model suitable for this discussion.
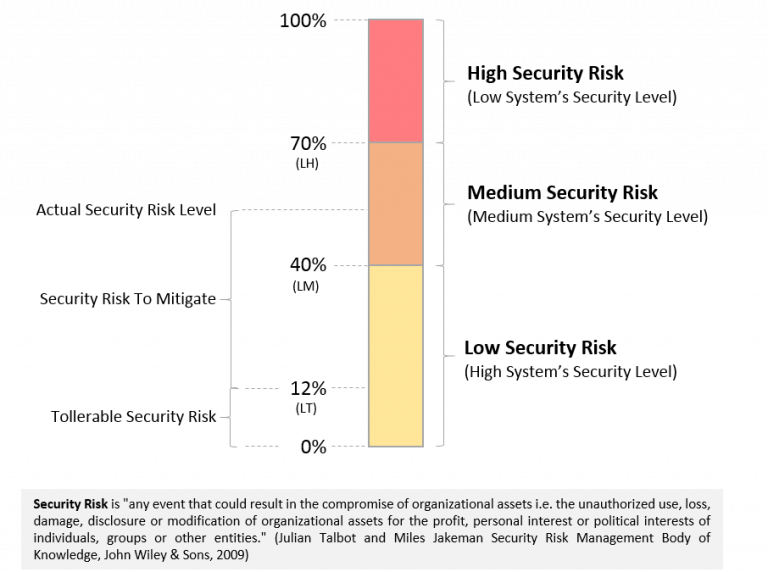
Figure 1 – cybersecurity risk metric (Security Level) model for business.
The cybersecurity risk metric can be used to measure an existing IT system’s actual risk exposure (its “security level”) or to define the maximum acceptable risk for a new system. It also helps identify the controls needed to reduce exposure from the actual level to the expected level. Cybersecurity risk measures can be quantitative (e.g., from 0 to 100) or qualitative (e.g., high, medium, low).
Figure 1 depicts some considerations that business (and technical) personnel in an organization should keep in mind when defining the cybersecurity risk metric or measuring the cybersecurity level of an IT system:
Based on these considerations, business stakeholders should not delegate all cybersecurity activities to their technical colleagues. They should instead play a key role in defining cybersecurity risk metrics so that they understand how well their IT systems are protected and how much budget they need to reduce actual risk to the maximum tolerable level.
When business stakeholders play this role, they can rephrase the initial question (“How secure is this IT system?”) and expect and understand a faster, more precise response. Their technical colleagues, on the other hand, should understand that cybersecurity is primarily a business matter, that it should not be used for political purposes within the organization, and that they should make every effort to ensure that business stakeholders help define the organization’s cybersecurity standards, provide requirements for the IT systems they own, and remain aligned with their technical colleagues.
Many business personnel have a clear understanding of what a penetration test or a vulnerability assessment is and they are confident that if the IT systems they own pass these tests/assessments, these systems are “secure.” However, this is not the case because a penetration test (an authorized, simulated cyberattack on an ICT system, also known as a pen test, pentest, or ethical hacking [2] [3]) can only evaluate a portion of the system’s security.
Let’s look at an example. An organization’s Customer Information System is managed by an untrustworthy system administrator who has access to all of the company’s customers’ data and sells it to the competition. Because of the system administrator’s role, he or she has default access to this system and data, and a penetration test is ineffective in identifying this security risk.
Cybersecurity is thus more than just penetration testing; it is a process for managing security risk throughout an IT system’s life cycle, and it includes many subprocesses such as security risk identification, analysis, evaluation, and treatment (mitigation). Cybersecurity metrics, as previously described, play a key role in this process and its subprocesses, as do business personnel.
[1] Julian Talbot and Miles Jakeman Security Risk Management Body of Knowledge, John Wiley & Sons, 2009.
[2] “What Is Penetration Testing?”, Retrieved 2018-12-18, Wikipedia.
[3] “Penetration Testing overview”. Retrieved 2019-01-25, Wikipedia.
[4] Software Security, Andrea DeSantis, 2020.
A basic checklist for hardening and optimizing a WordPress website.
Security vulnerabilities can provide valuable knowledge for business, technical, and operational decision-making.
A reference model for identifying software security vulnerabilities, with databases, metrics, and relationships among standards.
CONTINUE THE CONVERSATION
Share your perspective.
Comments are moderated before publication.